

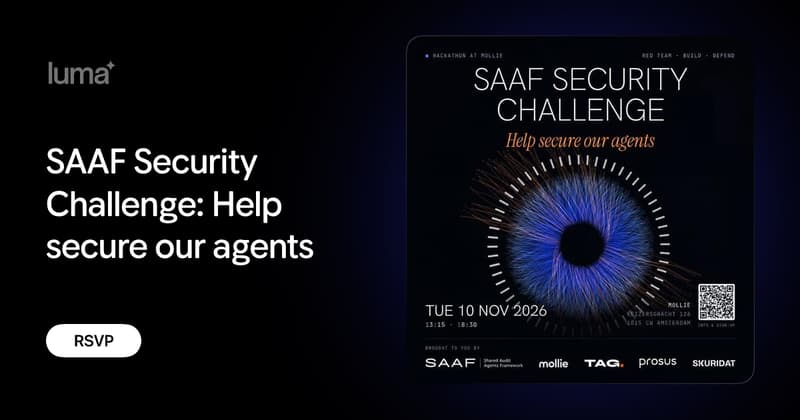
SAAF Security Challenge: Help secure our agents
Downloads an .ics file · Times are in Europe/Amsterdam · Google Calendar
A one-day hackathon on breaking and then hardening the AI agents now sitting inside audit, risk and compliance work. Red teams from Prosus and Skuridat attack the open-source agents of the Shared Audit Agents Framework live, and the room then builds the defences across the repository.
Around 100 auditors, developers and security specialists, deliberately mixed so people who know what an agent should never do sit with people who can make sure it doesn't. Brought together by TAG with SAAF, Mollie, Prosus and Skuridat, hosted by Ben vanLeeuwaarde and Tijs Nieuwboer.
Retimed by the organiser on 5 November: doors 13:15, programme 13:30 to 18:30. The start time shown above is wrong - it is 13:30, not 09:00. At Mollie, Keizersgracht 126. Registration needs host approval.
Why go: live adversarial testing of agents in a regulated workflow is rare, and rarer with the auditors in the room rather than in the review afterwards.
More like this near Amsterdam


Going to SAAF Security Challenge? Ask me anything about it.
I read the organiser's pages and answer in a few seconds.
Answers are AI-generated · Privacy