

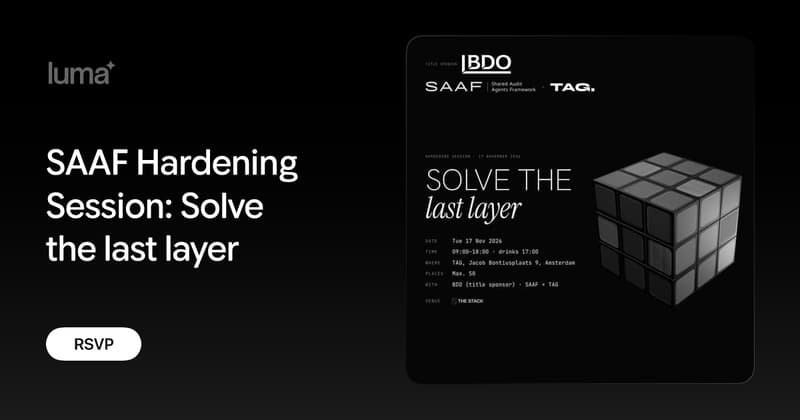
SAAF Hardening Session: Solve the last layer
Downloads an .ics file · Times are in Europe/Amsterdam · Google Calendar
The follow-up to the SAAF security challenge on 10 November, and the session where the open parts get closed. The agents, the audit criteria and the shared library are built; this day goes over every agent, fixes what the red teams found, and locks each fix in with a test.
Three strands run through the day: repairing agents, checking each one against its audit criteria pass or fail, and tightening access, logging and sign-off across the framework. SAAF brings auditors and builders from more than 65 organisations together to build AI agents for audit work in the open. Hosted by TAG at The Stack, with Ben vanLeeuwaarde, Sofia Frumkina, Tijs Nieuwboer and Mathijs Schouten. BDO is title sponsor.
Doors 09:00, hardening until 17:00, drinks to 18:00. Free, 50 places, 36 taken.
Why go: agents for regulated audit work get hardened with the auditors who sign them off in the room, not in the review afterwards. Best for security and platform engineers putting agents near compliance decisions.
More like this near Amsterdam


Going to SAAF Hardening Session? Ask me anything about it.
I read the organiser's pages and answer in a few seconds.
Answers are AI-generated · Privacy