
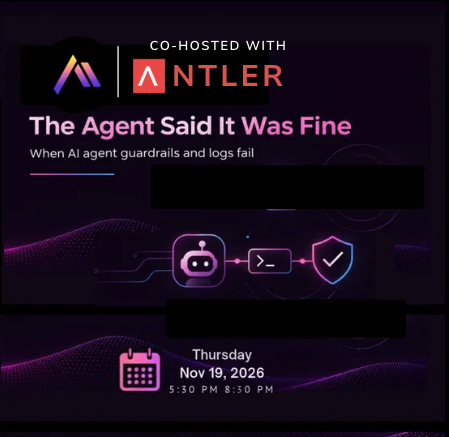
The Agent Said It Was Fine | AI Security Engineer Toronto
Downloads an .ics file · Times are in America/Toronto · Google Calendar
This is the third in-person event from AI Security Engineers Toronto or AISecEngTo. Come for the talks, stay for the argument.
Co-hostAntler
AI agents now run commands, call tools and touch production. The guardrails around them are supposed to keep them in line, and the logs they write are supposed to tell us what they did. This edition looks at what happens when neither holds up.
Talks
Bypassing Agent-Framework Guardrails: How I Vibe Coded a Scanner to Find 7 VulnerabilitiesAhmed KhanAhmed set out to hunt for bugs in MCP servers. He vibe coded a scanner, mcp-hunt, and ran it across 141 repos. It found no MCP bugs, but it did find one in an agent orchestration framework, which he disclosed and the maintainer patched (CVE pending). He then scanned the 1,000 most-used agent frameworks and MCP servers and came away with 7 vulnerabilities. This is the story behind them.
A Log Is a Story the Agent Told About Itself: Independently Verifying What AI Agents DidLei ZhouWhen an agent runs commands on your machine, the agent writes the record of what it did. Signing a log proves nobody altered it, not that it’s true. An action the agent never wrote down leaves nothing to sign. Lei presents anchorstamp, an open-source Rust proof of concept that checks each agent claim against an observer the agent can’t reach: the Linux kernel’s audit subsystem. The live demo covers an honest agent, a forged claim, a hidden action, and an agent trying to tamper with the evidence. Lei will also be clear about what this approach cannot prove.
What if developers could identify security vulnerabilities before their code even reaches the CI/CD pipeline?
Ashvin Ravi will introduce an AI-powered Security Audit Skill that analyzes source code repositories, identifies potential vulnerabilities, and maps findings to established frameworks such as OWASP Top 10 and MITRE ATT&CK.
He will also explore how this approach extends to AWS CDK repositories, generating actionable cloud security recommendations and helping developers integrate security earlier into the development lifecycle.
More on the speaker lineup soon.
Agenda5:30 PM Doors, food and networking6:00 PM Welcome6:10 PM Talks + Q&A7:30 PM Open discussion and networking8:30 PM Close
Thanks to our co-hosts, Antler for making this possible.
Free to attend. Space is limited, so please register so we can plan for food. If you can’t make it, free up your spot.
AISecEngTO is a volunteer-run community for people working where AI and security meet: practitioners, researchers, builders and the curious.
More like this near Toronto


Going to The Agent Said It Was Fine? Ask me anything about it.
I read the organiser's pages and answer in a few seconds.
Answers are AI-generated · Privacy